An interpretation of the recorded conversation.
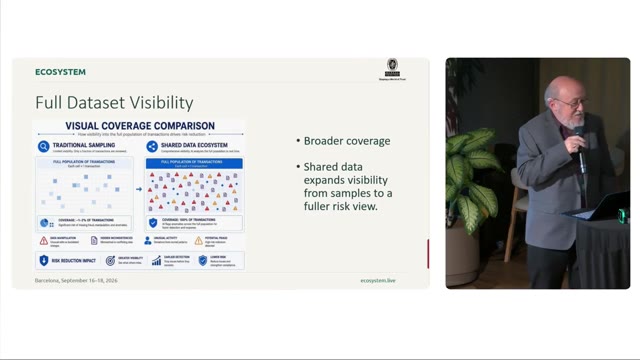
Chuck Rogers speaks from Bureau Veritas Consumer Product Services and prior retail/manufacturing experience. The central case is a recalled product that passed sampled testing because the sample came from a different input source than the contaminated batch. It distinguishes a supplier map from lot-level evidence linking particular inputs to outputs. Testing earlier, where a relevant characteristic is established, is proposed to avoid discovering defects only after further production and distribution.
The approach combines verified chain-of-custody procedures, contemporaneous conversion records and risk-based checks. Chuck explicitly says verifying every document is impractical. A content-certification mark is being launched, with a car-seat recycling project described as an initial case. This is distinct from existing broad schemes and from a fully deployed continuous-assurance model. Neither a specific material-content claim nor a traceability record proves total sustainability.
The future social-audit model would reuse verified datasets and ongoing payroll analysis, reserving auditors' time for contextual observation and interviews. The claim is that better information can target attention and detect errors sooner. A small reported pilot analysed a factory's payroll and found issues missed by sampling; the factory permitted the experiment, and the findings were corrected outside the formal audit report. Reported time figures vary within the telling and must not become a precise benchmark. No false-positive rate, ground-truth validation or independent pilot evaluation is supplied.
The crucial institutional qualification is competitive: if one auditor detects more nonconformances, clients may avoid it. Better technology therefore requires scheme-level coordination, not merely a more capable individual verifier. Human sign-off is described as organisational policy, and checking whether reviewers notice seeded errors is discussed as a possible way to avoid rubber-stamping. That is a proposal, not an established validated safety system.
Audience questions expose two limits. Asked how much complexity human decision makers can manage, the response explains the value of earlier intervention but does not directly test cognitive usability. Asked about risks of shared systems, the response emphasises trust and permissions, then identifies unequal incentives: growers reportedly pay for improvements and supply data without receiving premiums, feedback or clarity about use. Reciprocal information and rewards are proposed; neither actual payments nor effective control are demonstrated in this talk.
The return to the recall case shows costs concentrating on the first-tier supplier after other actors have been paid. Visibility may reveal a causal chain without automatically reallocating legal or financial liability. Supplier losses, product facts, regulatory statements and numerical examples are attributed and unverified. The talk is both practitioner evidence and a positive commercial partnership account.
 2:36